Website Security Check
For business websites and portals. Passive checks, exposed-information review, configuration observations, and a concise findings summary.
Discuss this package ↗Independent security researcher · Ghana
I help Ghanaian businesses and organizations identify web-application vulnerabilities through authorized, controlled security assessments—with clear reports and practical remediation guidance.
01 / Services
Choose a focused review or start with a conversation about your application, priorities, and budget. Scope, targets, credentials, timeline, and deliverables are agreed before testing begins, so pricing is quoted per engagement.
For business websites and portals. Passive checks, exposed-information review, configuration observations, and a concise findings summary.
Discuss this package ↗For login-based applications and dashboards. Authorized testing of authentication, access control, sessions, input handling, and core workflows.
Discuss this package ↗For products with mobile or public APIs. Endpoint inventory, authorization checks, validation review, and a prioritized report.
Discuss this package ↗For teams that have applied fixes. Follow-up checks and a verification note showing which findings were resolved within the agreed scope.
Discuss this package ↗02 / Your report
A redacted sample report is being prepared. The final format is designed to help both decision-makers and developers understand what matters next.
The sample will be published here when a suitable redacted example is available. No client identity or confidential finding is shared without permission.
03 / Why organizations choose Gisbounty
More than 200 security reports have been written across private research and client-facing work. Because reports and client praise are confidential, names, screenshots, and quotes are shared only when the owner gives permission.
Private references and redacted evidence can be discussed when appropriate.
Every active assessment begins with written authorization and a defined scope.
Testing methods and prohibited actions are agreed in advance to minimize disruption.
Reports explain business impact, evidence, and prioritized next steps—not just technical labels.
Talk through remediation and arrange retesting when your fixes are deployed.
Testimonials are available for private review; public quotes wait for written permission.
Reports can be redacted for learning and portfolio use without revealing client identities or sensitive findings.
04 / How it works
Share your application type, goals, concerns, and the systems you want reviewed.
Agree in writing on permitted targets, methods, timeline, and reporting expectations.
Carry out the agreed checks, validate findings safely, and minimize disruption.
Receive actionable findings, discuss fixes, and request optional retesting.
05 / Selected work
Alongside research, I build practical web projects focused on digital tools, security education, and accessible learning.
A cloud-style project for storing and organizing information online.
Explore project ↗SECURITY PRACTICEAn educational environment for hands-on ethical hacking and bug bounty concepts.
Explore project ↗LEARNING PLATFORMVideo-based content and resources for responsible security learning.
Explore project ↗06 / Certificates
Selected certificates and completed assessments that support my ongoing work in cybersecurity and responsible security research.
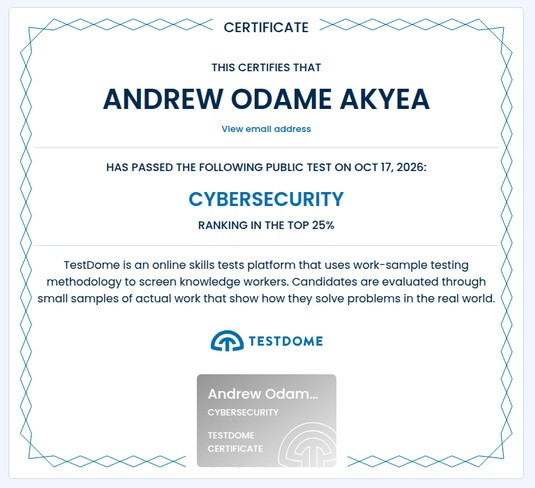
Verified certificate from TestDome.
Andrew Odame Akye...CybersecurityTestDome06 / About Gisbounty
I’m an independent security researcher offering authorized website and web-application assessments, responsible-disclosure support, and remediation guidance. I also design and build responsive web projects with secure development fundamentals in mind.
07 / FAQ
No. Active testing starts only after the owner or an authorized representative gives written permission and the target scope is agreed.
Usually the target URLs or app details, your goals, test accounts or credentials where needed, an authorized contact, prohibited actions, and the preferred timeline.
The approach and prohibited actions are agreed in advance. Testing is controlled and designed to minimize disruption, but no assessment can promise zero operational risk.
The goal is to avoid unnecessary access. If data exposure is relevant to a verified finding, it is handled minimally, documented responsibly, and reported privately.
Timing depends on the number of targets, application complexity, access provided, and agreed scope. A realistic timeline is discussed before work begins.
Scope and authorization, validated findings, severity context, affected features, safely redacted evidence, impact, and practical remediation guidance.
Yes. Follow-up verification can be scoped after fixes are deployed to confirm whether reported findings were resolved.
Yes, when the report concerns a platform that you are authorized to represent. Please use the contact details below and include enough context for a safe, private response.
READY WHEN YOU ARE
Tell me what your website does and what kind of help you’re looking for. We can start with a scoped conversation.
Assessments are conducted only with the website owner’s permission and an agreed scope. No guarantee of a vulnerability-free website is implied. One phone contact · two email options.